07 · Service line

Security & Compliance

Penetration testing, OWASP MASVS assessments, secure code review and compliance readiness for HIPAA, SOC 2 Type II, GDPR and PCI-DSS, whether we built the app or not.

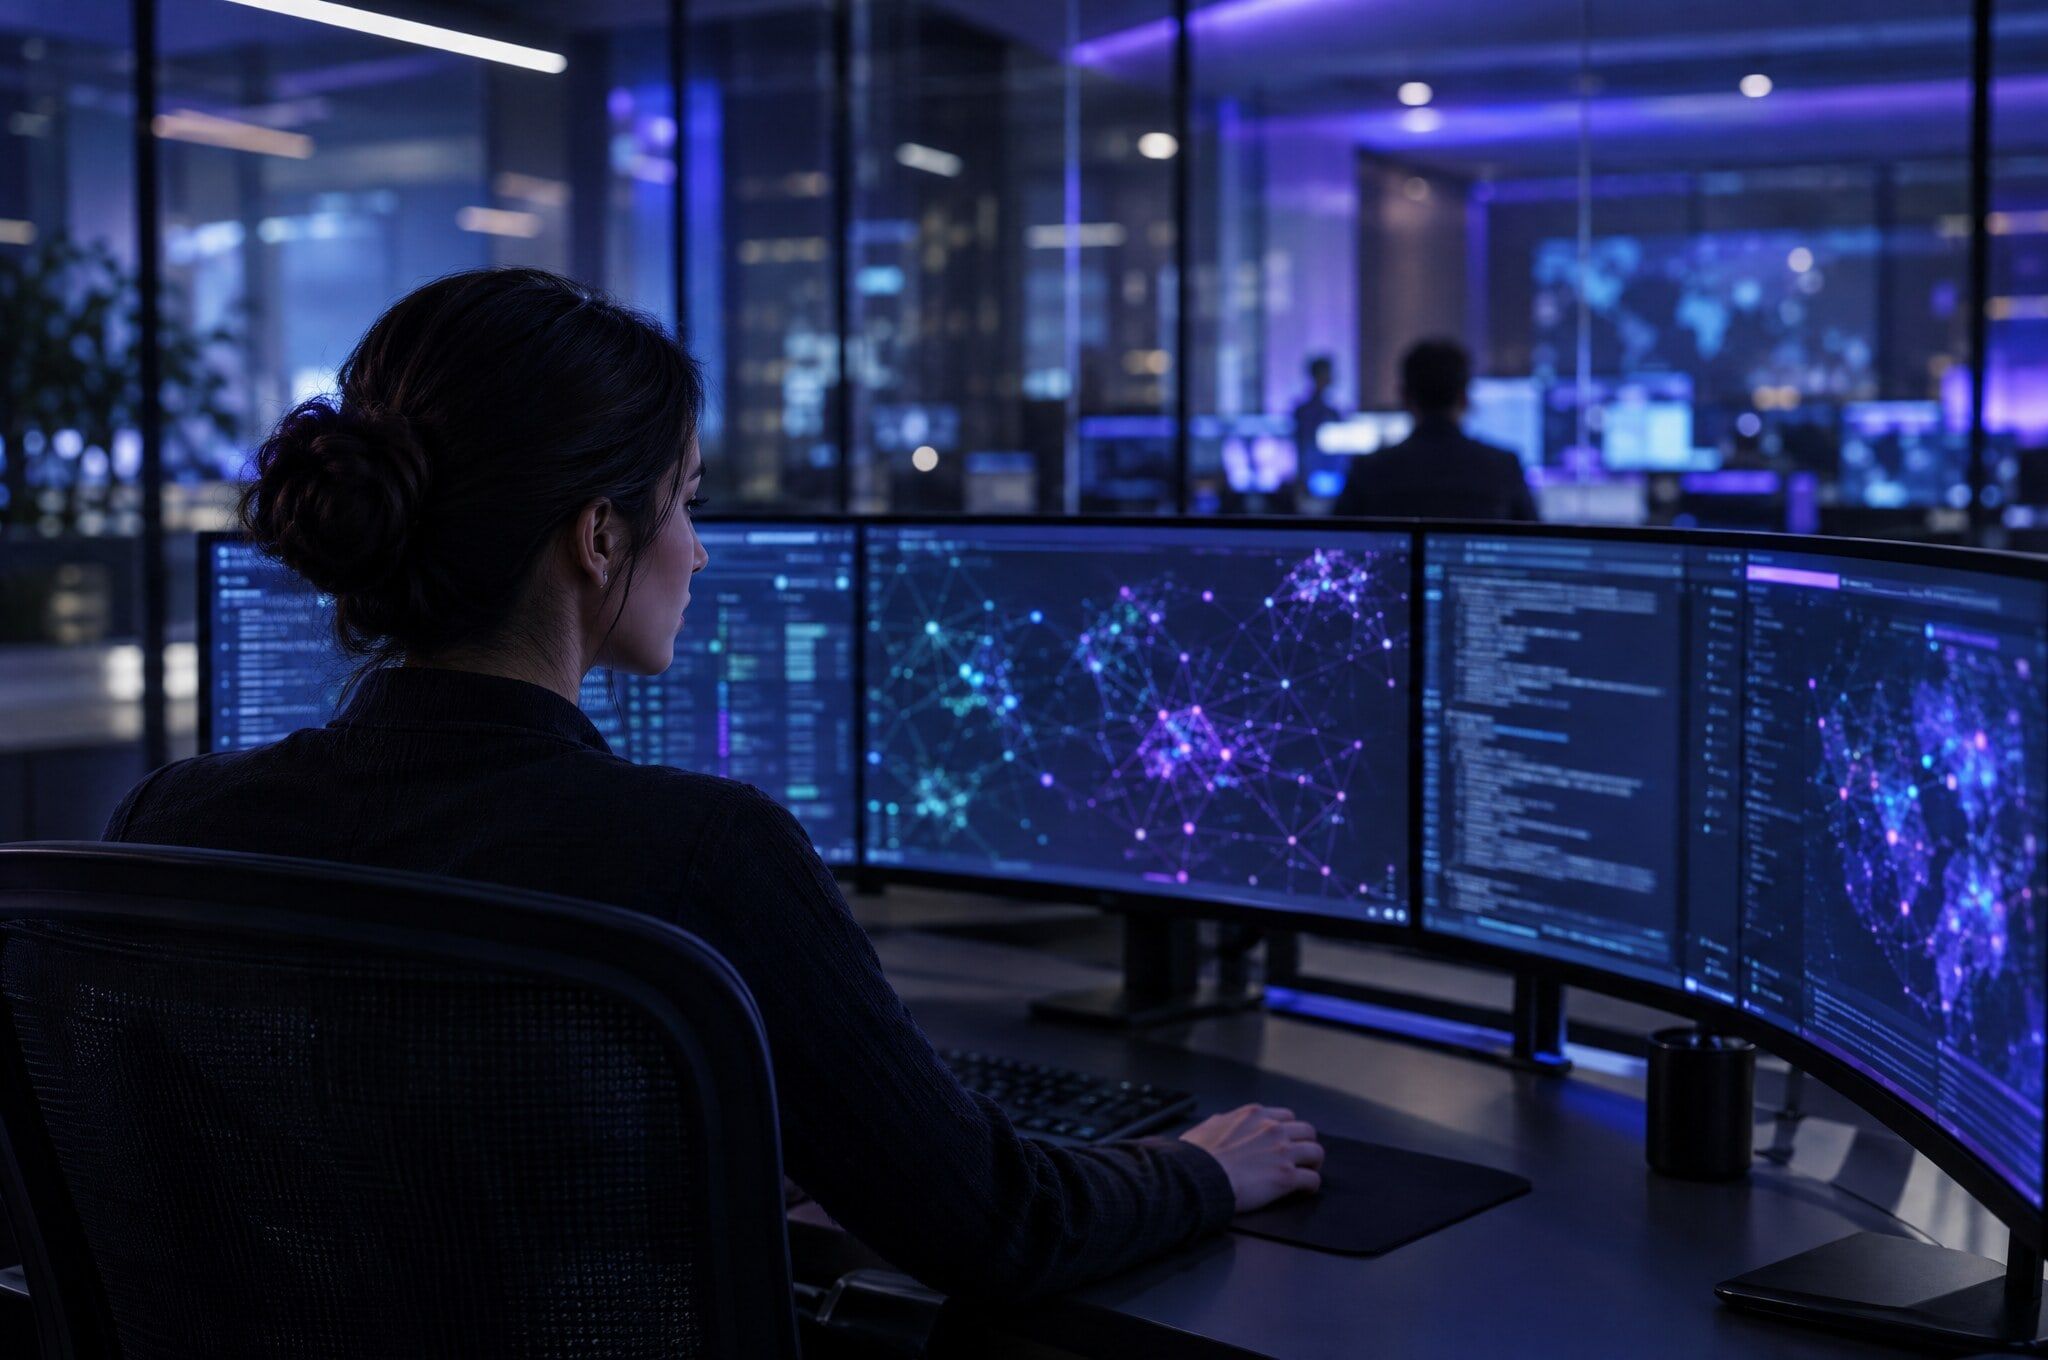
A security analyst in front of curved monitors showing network graphs

What's included

Independent testing and readiness for regulated launches.

07.1

Penetration testing: app, API & cloud

Find what an attacker would, before they do.

Manual and tool-assisted testing of the mobile client, its APIs and the cloud behind them, with exploitability-rated findings and retesting after fixes.

Deliverables

  • Scoping and rules of engagement
  • Rated findings with reproduction steps
  • Remediation retest and attestation letter
07.2

OWASP MASVS assessments

Measured against the mobile security standard.

Assessment against the OWASP Mobile Application Security Verification Standard covering storage, cryptography, authentication, network, platform and resilience controls.

Deliverables

  • MASVS control-by-control results
  • Gap analysis
  • Prioritized remediation roadmap

07.3

HIPAA, SOC 2, GDPR & PCI-DSS readiness

Ready for the audit, not surprised by it.

We map regulatory requirements to app and infrastructure controls, close the gaps and assemble the evidence your auditors and customers will ask for.

Deliverables

  • Control mapping and gap assessment
  • Policy and technical remediation
  • Audit evidence package

07.4

Secure code review

Vulnerabilities caught at the source.

Line-by-line review of high-risk code paths combined with static and dependency analysis, with fixes your developers can apply immediately.

Deliverables

  • Threat model of critical flows
  • Code-level findings
  • Secure coding guidance for your team

How we run it

A clear process, every engagement.

  1. 01

    Scope

    Agree targets, rules of engagement and the standards in play.

  2. 02

    Test

    Assess the client, APIs and cloud with manual and automated techniques.

  3. 03

    Report

    Deliver rated findings with clear reproduction and fix guidance.

  4. 04

    Retest

    Verify fixes and provide an attestation for stakeholders.

Standards & frameworks

OWASP MASVSOWASP MASTGHIPAASOC 2 Type IIGDPRPCI-DSS
How we approach compliance

Available standalone

Book a penetration test, a MASVS assessment or a readiness review for any app, built by anyone.

Scope it with us

20 years of mobile engineering

Tell us what you are building.

Share the platforms, compliance needs and budget. Programs over $50k go straight to an engineering lead.

  1. 01

    We read every requestAn engineering lead reviews your brief, not a sales queue.

  2. 02

    Programs of $50k or more go to an engineering leadNot a sales queue: a lead reviews the brief and contacts you to set a time.

  3. 03

    You get a planArchitecture options, team shape and a phased estimate.