HIPAA-compliant architecture
Encryption in transit and at rest, minimum-necessary data access, audit logging and breach-ready incident processes.
Services
We modernize outdated apps, add AI to them and build new ones, with every service around the app under one roof. Each can be commissioned on its own.
All servicesModernize
Service lines
Industries
Dedicated practices for regulated healthcare, enterprise operations and consumer products, with enterprise as our core focus.
All practicesPractices
Organizations
Security & compliance
How we protect your code and data, and how we engineer apps to HIPAA, SOC 2 Type II, GDPR, PCI-DSS and OWASP MASVS.
Trust & securityCompany
Twenty years of researching, designing, building, testing and securing mobile software.
All contact optionsPrimeServ
Services
We modernize outdated apps, add AI to them and build new ones, with every service around the app under one roof. Each can be commissioned on its own.
All services →Modernize
Service lines
Industries
Dedicated practices for regulated healthcare, enterprise operations and consumer products, with enterprise as our core focus.
All practices →Practices
Organizations
Security & compliance
How we protect your code and data, and how we engineer apps to HIPAA, SOC 2 Type II, GDPR, PCI-DSS and OWASP MASVS.
Trust & security →Company
Twenty years of researching, designing, building, testing and securing mobile software.
All contact options →PrimeServ
Regulated practice
Clinical and patient-facing apps where privacy, auditability and reliability are requirements from the first sprint, not checkboxes at the end.
Where we focus
Encryption in transit and at rest, minimum-necessary data access, audit logging and breach-ready incident processes.
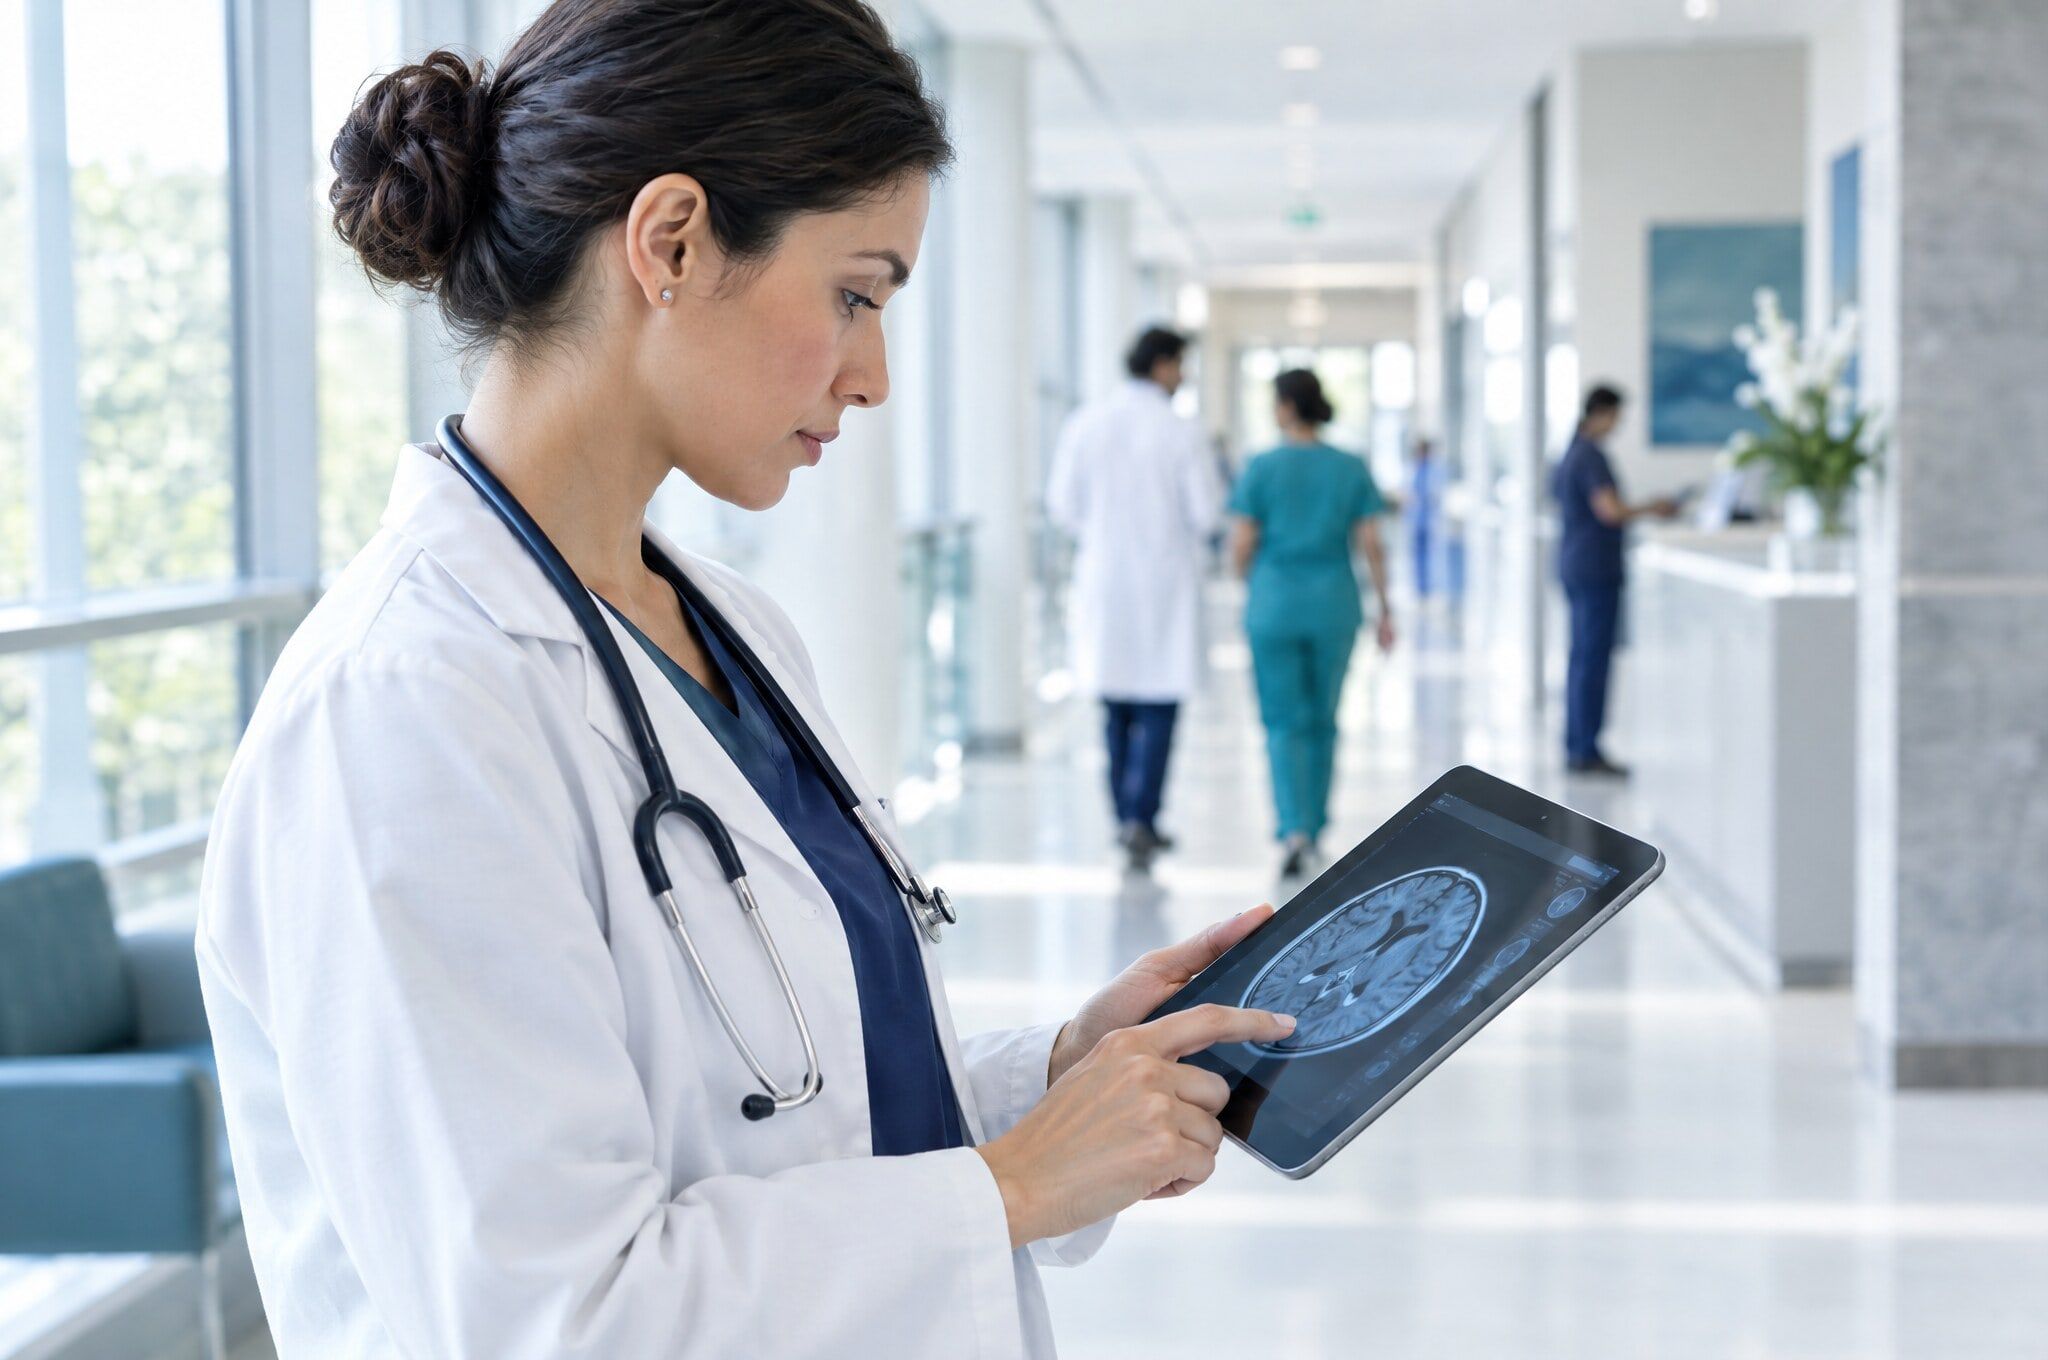
Performant medical image viewing with measurement, annotation and comparison tools on tablets and large screens.
Standards-based integrations with electronic health records, scheduling and clinical systems.
Consent management, data retention, de-identification and secure sharing between care teams.
Representative app types
Typical healthtech work includes: telehealth and virtual care, clinical imaging review, patient engagement and intake, care-team coordination.
Telehealth visitPhone · HealthTech
Stack: Swift · KotlinResearch behind it: Patient journey researchStandard tested to: HIPAAOperational fit: EHR integrationRevenue model: Per-visit billing
Imaging reviewTablet · HealthTech
Stack: Native iPadOS · DICOMResearch behind it: Clinician usability testingStandard tested to: HIPAA · DICOMOperational fit: Works offline on the wardRevenue model: Enterprise license
Compliance & standards
| Standard | Where it applies | Our role |
|---|---|---|
| HIPAA | Healthcare apps handling protected health information | Architecture, safeguards, audit logging and readiness evidence |
| SOC 2 Type II | Enterprise and workforce platforms | Control-aligned access, change management and audit preparation |
| GDPR | Apps with users in the EU and UK | Consent, data minimization, residency and erasure workflows |
| OWASP MASVS | Every app we build or test | Security requirements, assessments and penetration testing |
| WCAG 2.2 | Every app we design | Accessible design and conformance audits |
| DICOM | Medical imaging | Image viewing, measurement and markup |
Key services
20 years of mobile engineering
Share the platforms, compliance needs and budget. Programs over $50k go straight to an engineering lead.
We read every requestAn engineering lead reviews your brief, not a sales queue.
Programs of $50k or more go to an engineering leadNot a sales queue: a lead reviews the brief and contacts you to set a time.
You get a planArchitecture options, team shape and a phased estimate.