In-app assistants
Answers drawn from your own documents and data, with sources shown and permissions respected.
Services
We modernize outdated apps, add AI to them and build new ones, with every service around the app under one roof. Each can be commissioned on its own.
All servicesModernize
Service lines
Industries
Dedicated practices for regulated healthcare, enterprise operations and consumer products, with enterprise as our core focus.
All practicesPractices
Organizations
Security & compliance
How we protect your code and data, and how we engineer apps to HIPAA, SOC 2 Type II, GDPR, PCI-DSS and OWASP MASVS.
Trust & securityCompany
Twenty years of researching, designing, building, testing and securing mobile software.
All contact optionsPrimeServ
Services
We modernize outdated apps, add AI to them and build new ones, with every service around the app under one roof. Each can be commissioned on its own.
All services →Modernize
Service lines
Industries
Dedicated practices for regulated healthcare, enterprise operations and consumer products, with enterprise as our core focus.
All practices →Practices
Organizations
Security & compliance
How we protect your code and data, and how we engineer apps to HIPAA, SOC 2 Type II, GDPR, PCI-DSS and OWASP MASVS.
Trust & security →Company
Twenty years of researching, designing, building, testing and securing mobile software.
All contact options →PrimeServ
20 years App modernization & engineering
For two decades we have brought apps forward: a modern redesign, a rebuild on native or cross-platform technology, and AI features your users will actually use. Testing, security and HIPAA, SOC 2 Type II, GDPR and PCI-DSS readiness come built in, and new apps get the same team.
Today’s medication
Representative app types, designed for illustration.
App modernization
Much of our work begins with an app that has fallen behind: a dated design, a framework nobody wants to maintain, releases that take too long. We redesign it, rebuild it on modern technology and add AI where it helps, while your users keep working.
We review the code, design, data and risks, then give you a clear path and an estimate.
Current platform conventions, adaptive layouts for every screen and accessibility built in.
Native or modern cross-platform, released module by module while your users keep working.
Assistants, smart search and automation wherever they make the app more useful.
AI integration
We add AI where it makes the app genuinely more useful: answering questions from your own content, summarizing records, reading documents and photos, and personalizing what each person sees. Private by design and measured before it ships.
Answers drawn from your own documents and data, with sources shown and permissions respected.
Find anything in plain language, and turn long records into a few clear lines.
Scan, recognize and transcribe, on the device itself when privacy calls for it.
Accuracy measured before every release; quality, speed and cost watched after launch.
Your data stays under your controlHIPAA-aware handlingWorks inside the app you already have
Services
Security and quality services apply to any app, including ones built by other teams. Ask for a penetration test or a device-lab QA pass without a build engagement.
Technology
Chosen per product: native where the platform matters most, shared code where it serves the roadmap. Adaptive layouts for phone, tablet and foldable are a requirement, not a stretch goal.
Swift and SwiftUI, multi-pane layouts, on-device machine learning.
Kotlin and Jetpack Compose, foldable-aware layouts, managed device fleets.
React Native and Flutter, with native modules where performance demands them.
Offline-first sync, Bluetooth LE, camera, payments, EHR and HR integrations.
Compliance · Security · Accountability
HIPAA, SOC 2 Type II, GDPR and PCI-DSS requirements mapped to app and infrastructure controls, with evidence collected as we build.
Penetration testing of app, API and cloud plus OWASP MASVS assessments, by engineers who did not write the code.
Dedicated teams join your repositories, pipelines and rituals, with least-privilege access and contracts that match the risk.
Who we serve
Large organizations are our core focus, and we bring the same senior team and standards to mid-sized companies, small businesses and startups.
Mobile programs for large organizations, delivered with the governance, security and scale procurement expects.
A senior mobile team on demand, so you can ship an exceptional product without building a department first.
Learn more Same team, same standardsThe same senior people and standards our largest clients get, scaled to the size of your team.
Learn more From first release to scaleA senior team to validate, build and scale a product your customers and partners will trust.
Learn moreDedicated practices
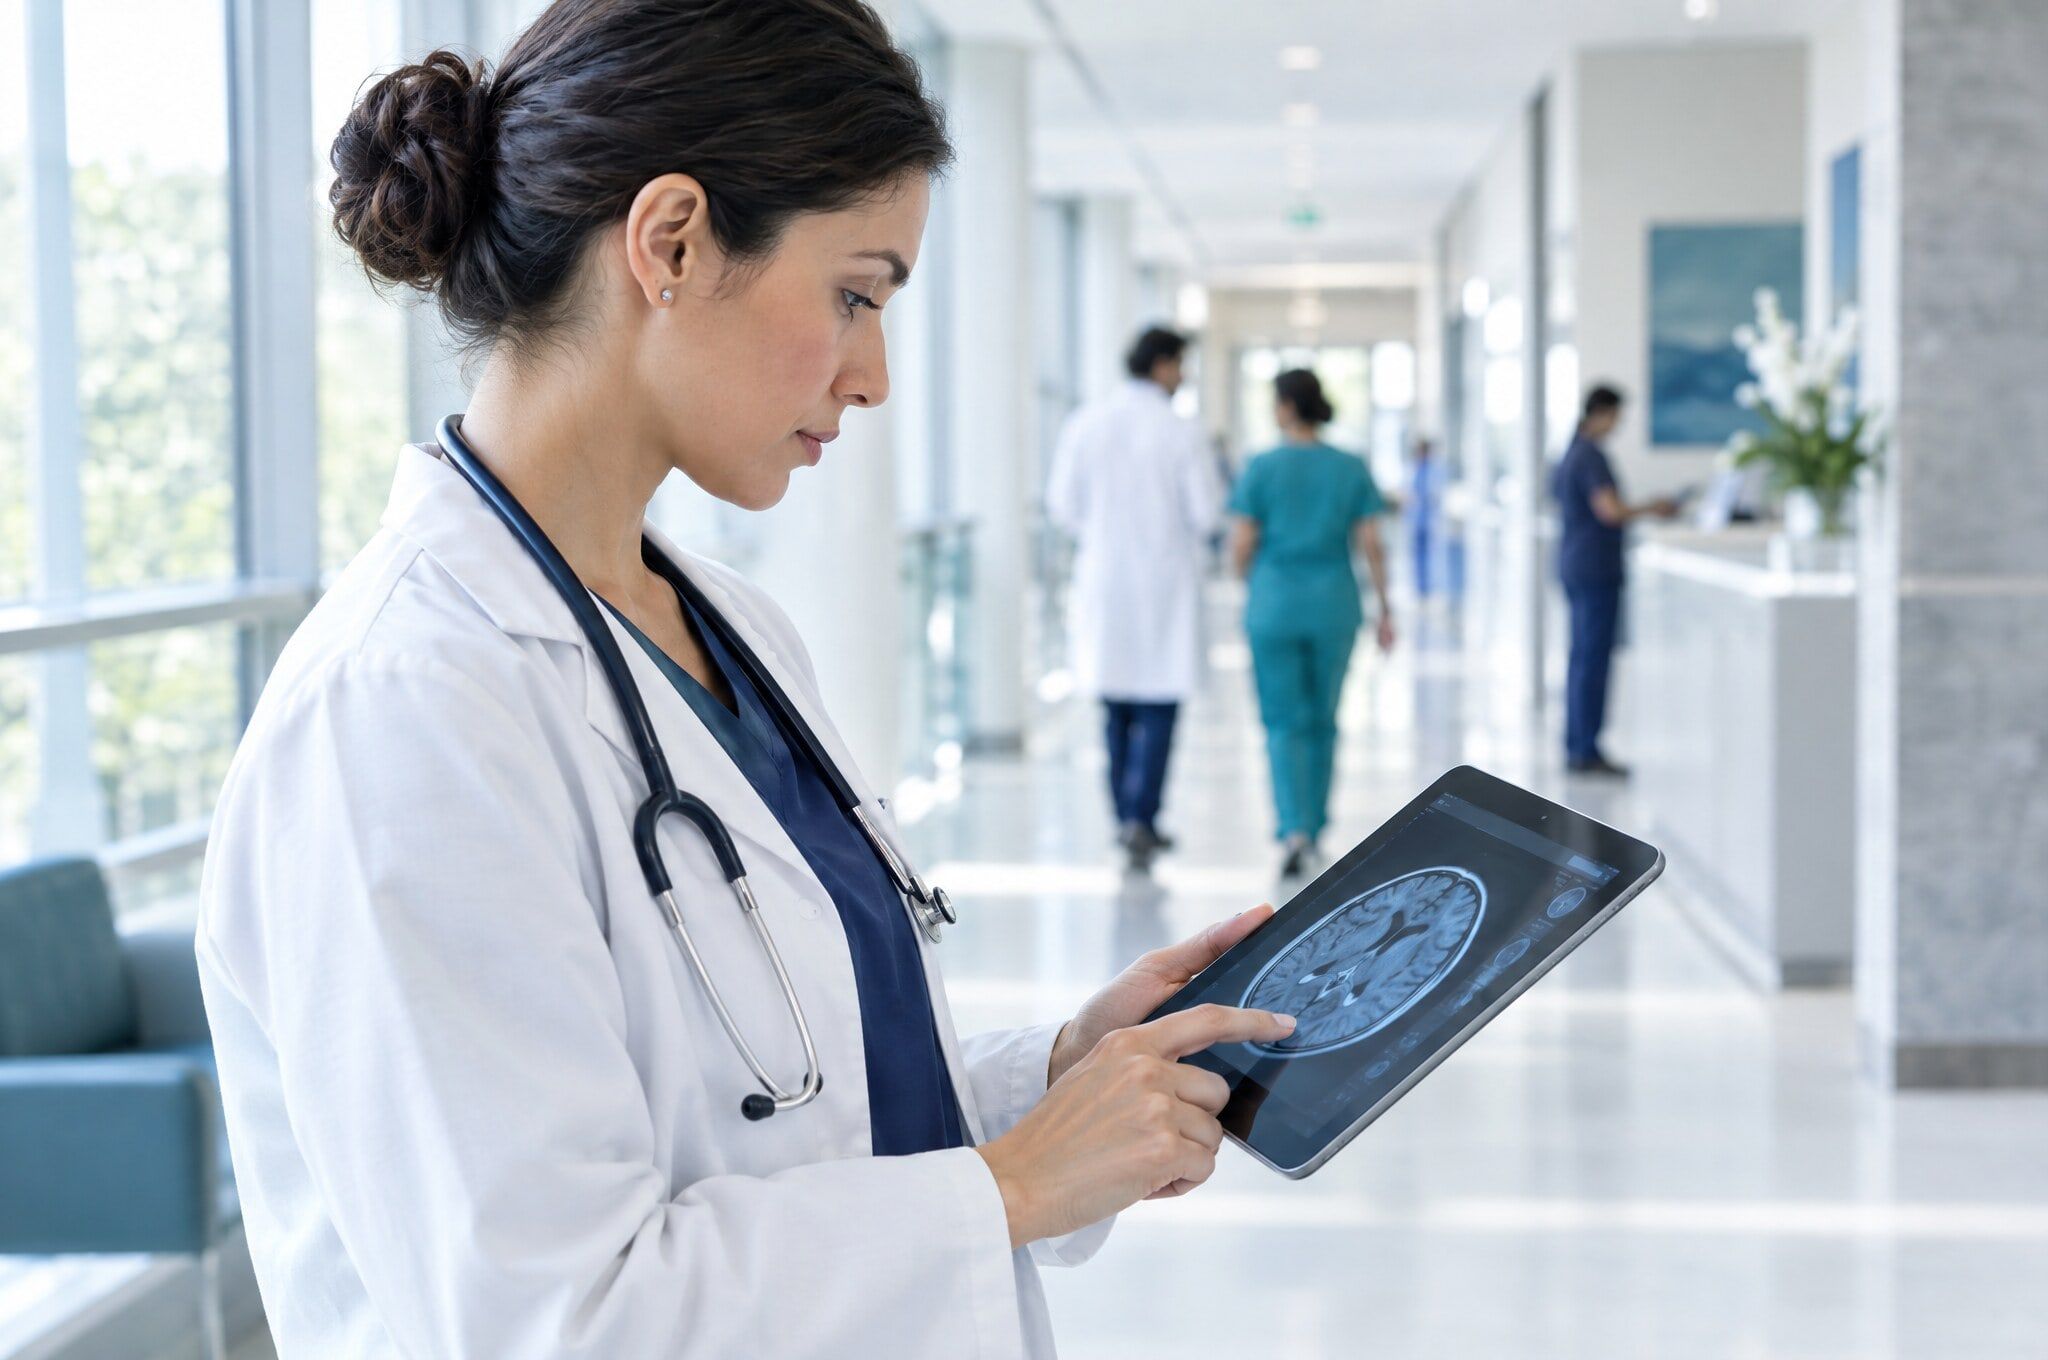
HIPAA-compliant architecture, DICOM viewing and medical image markup, EHR integrations and secure data handling.
Operational scaling, staff chat, HR integrations and SOC 2 Type II–compliant workflows for distributed teams.
High-engagement mobile games, booking engines and fluid consumer UX/UI across every form factor.
Engagement models
Start with a standalone service, embed a dedicated team, or hand us the whole product. Every model runs on the same delivery standards.
Strategy through launch and beyond, with one accountable team and one plan.
Best for: New products and major rebuilds
Engineers, QA and designers embedded in your roadmap, tools and rituals.
Best for: Enterprise programs and roadmaps that need capacity
A penetration test, market study, QA program or audit on its own.
Best for: Specific needs, any app, built by anyone
Monitoring, maintenance and OS-update readiness with defined service levels.
Best for: Live apps that must stay healthy and current
20 years of mobile engineering
Share the platforms, compliance needs and budget. Programs over $50k go straight to an engineering lead.
We read every requestAn engineering lead reviews your brief, not a sales queue.
Programs of $50k or more go to an engineering leadNot a sales queue: a lead reviews the brief and contacts you to set a time.
You get a planArchitecture options, team shape and a phased estimate.